Declared request shape
Only the agreed source profile and JSON request shape are accepted. Route, method, format and size checks happen at the boundary.
Ingress Shield // Solution brief v5.2
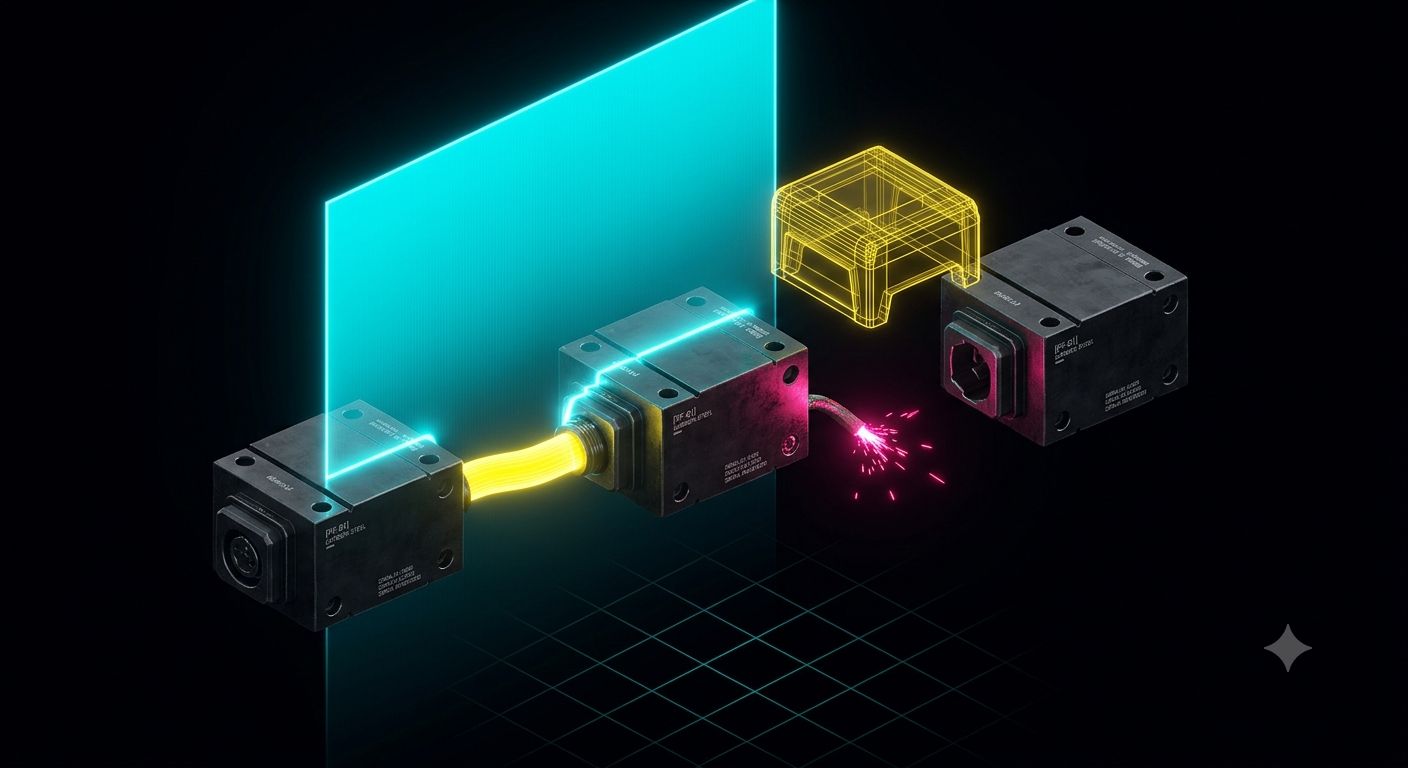
Built on Atom Flux foundations, this controlled pilot has two surfaces: Agent Preflight is a bounded, account-scoped, read-only MCP interface that helps approved AI coding and agent clients check whether a proposed tool chain, API or webhook connection, or workflow draft is compatible before action; Webhook Boundary protects declared webhook traffic on a reviewed route.
01 // the problem
AI-agent tool chains often break at the hand-off: a field is missing, an output is stranded, two tools expect different formats, or an assumed adapter is not actually present. Discovering that only after a workflow reaches a sensitive system creates rework and uncertainty about what may safely happen next.
Agent Preflight makes the first question bounded and read-only: do these declared tools and workflow drafts fit? It returns a redacted compatibility result and a clear next action for human review. It does not reveal secrets or payloads, change the workflow, or grant permission to run work.
02 // Agent Preflight
Approved coding and agent clients can use a bounded, account-scoped, read-only interface to check whether declared tool connections fit, review a workflow draft, compare safe drafts, or read a caller-owned result.
The interface cannot access secrets, configure webhook destinations, sign policies, queue or execute work, activate a workflow, or make arbitrary network calls.
02A // more than schema validation
Agent Preflight is more than a field-level schema check. A schema validator can confirm that one message has the expected shape; Preflight checks whether the declared hand-off makes sense in context: whether an input has a producer, an output has a consumer, an adapter is declared, and the connection has a review boundary.
Built on Atom Flux foundations, each result is tied to declared component and interface identities, explicit boundaries and a redacted review record. It does not compose, approve, sign or run the workflow.
03 // Webhook Boundary
Only the agreed source profile and JSON request shape are accepted. Route, method, format and size checks happen at the boundary.
For an approved pilot, accepted traffic goes only to one predeclared HTTPS sandbox destination with bounded retry.
Outcomes retain a reason code, timestamp and digest. Secrets and raw customer payloads do not become routine diagnostics.
04 // practical use cases
These are illustrative ways a team could use the controlled pilot. They describe connection checking and review, not a claim of framework integration or automatic execution.
Check whether each declared tool supplies the fields and format the next tool expects. Flag a missing input, a stranded output or an explicit adapter that is needed before the chain is reviewed.
Verify a declared source, route, method and request shape before a sandbox receiver or agent workflow is allowed to inspect the event.
Return a bounded next action—add a field, correct the expected schema, insert an explicit adapter or request review—without silently changing the workflow.
Bring related declared checks into one ordered, redacted review pack: what fits, what stopped, and the next action for a person. It does not approve, deploy or run the change.
05 // review-led onboarding
Start with a sandbox webhook or agent-tool use case. Do not send credentials, private keys, personal data or confidential payloads. WorkFoundry agrees scope, data boundary and secure onboarding separately; any change beyond the controlled pilot is a separate human decision.
06 // common questions
It checks whether declared tools, a proposed API or webhook connection, or a workflow draft fit before action. The result is bounded, redacted and intended to support human review.
No. It does not reveal secrets or payloads, change a workflow, sign policy, queue work, activate a workflow or grant permission to run work.
No. For an approved pilot it accepts only the agreed source profile and request shape on a reviewed route, then delivers only to one predeclared HTTPS sandbox destination with bounded retry.
Start with a public-safe outline of a sandbox webhook or agent-tool use case. Do not send credentials, private keys, personal data or confidential payloads. WorkFoundry agrees scope, data boundary and secure onboarding separately.
07 // pilot identity and privacy
The closed-pilot onboarding design uses Auth0-brokered Google or Microsoft browser sign-in. WorkFoundry does not receive provider passwords, and the intended gateway record is pseudonymous rather than an email or profile record.
The protected MCP endpoint is deployed, but no external OAuth client, pilot invite, user account or browser-client acceptance has been completed. An external identity will not grant access by itself. Read current pilot privacy information.